
OWASP Top 10 2025: Web Vulnerabilities Explained with Examples
The 10 categories of the OWASP Top 10 2025 explained with code examples, what changed since 2021, and how to protect your web app.
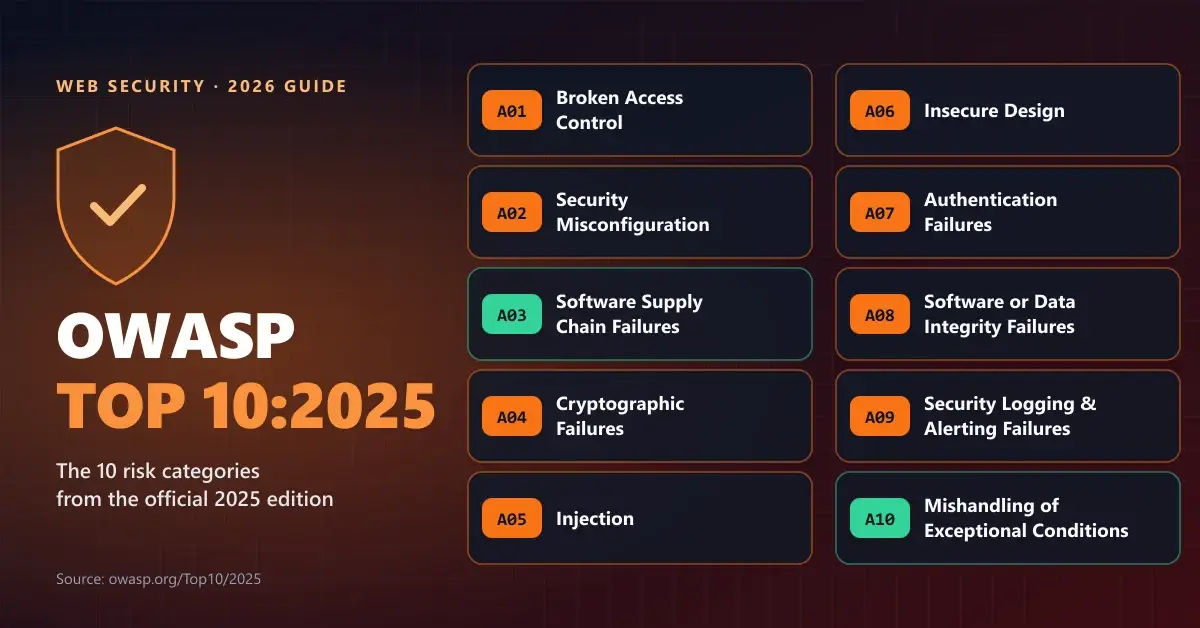
How many applications does it take to know what’s going wrong in web security? For its latest edition, OWASP analyzed data from more than 2.8 million applications. The result confirms something uncomfortable: the most common failures aren’t sophisticated attacks, but design and configuration oversights.
The good news is that almost all of them can be prevented if you know where to look.
In this guide you’ll find the 10 categories of web vulnerabilities in the OWASP Top 10 2025, explained with code examples, what changed from the 2021 list, and a checklist to review your next project.
What Is the OWASP Top 10 and What Is It For?
OWASP (Open Worldwide Application Security Project) is a nonprofit foundation that publishes open guides, tools, and standards for software security. Its best-known project is the Top 10: an awareness document listing the most critical risks to web applications.
The 2025 edition is the eighth. It groups 248 weaknesses (CWEs) into 10 categories. Eight come from data contributed by companies and analysts, and two from a survey of the security community, to capture new risks the data doesn’t reflect yet.
Important: the Top 10 is a starting point, not a certification. If you need to verify an application in depth, OWASP recommends its ASVS (Application Security Verification Standard), which is far more detailed.
What Changed from the OWASP Top 10 2021 to 2025?
There are two new categories, one merger, and several position changes:
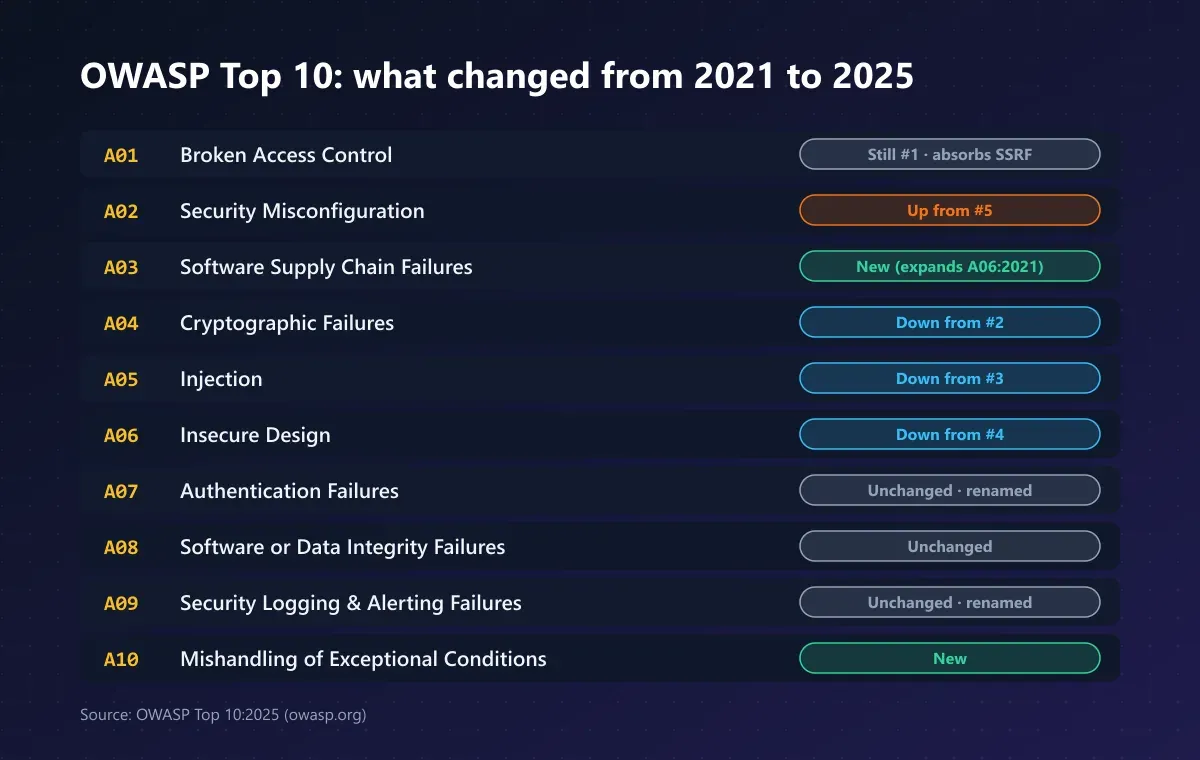
| 2025 rank | Category | In 2021 |
|---|---|---|
| A01 | Broken Access Control | #1 (now includes SSRF, previously #10) |
| A02 | Security Misconfiguration | #5 |
| A03 | Software Supply Chain Failures | New (expands “Vulnerable Components,” #6) |
| A04 | Cryptographic Failures | #2 |
| A05 | Injection | #3 |
| A06 | Insecure Design | #4 |
| A07 | Authentication Failures | #7 (renamed) |
| A08 | Software or Data Integrity Failures | #8 |
| A09 | Security Logging & Alerting Failures | #9 (renamed) |
| A10 | Mishandling of Exceptional Conditions | New |
The 10 OWASP Top 10 2025 Categories Explained
A01: Broken Access Control (Now Including SSRF)
Still in first place. It happens when a user can view or modify data that isn’t theirs. The classic case is IDOR: changing a number in the URL and accessing someone else’s account.
// ❌ Vulnerable: anyone with a session can read any invoice
app.get('/api/invoices/:id', requireLogin, async (req, res) => {
  const invoice = await db.invoices.findById(req.params.id);
  res.json(invoice);
});

// ✅ Secure: the server checks that the invoice belongs to the user
app.get('/api/invoices/:id', requireLogin, async (req, res) => {
  const invoice = await db.invoices.findOne({ id: req.params.id, userId: req.user.id });
  if (!invoice) return res.status(404).end();
  res.json(invoice);
});
In 2025 this category absorbs SSRF (Server-Side Request Forgery): when your server fetches a URL chosen by the attacker and ends up reaching internal services. The defense is validating URLs against an allowlist of destinations.
A02: Security Misconfiguration
The category that climbs the most among existing ones: from #5 to #2. It covers unchanged default passwords, debug mode left on in production, publicly open cloud buckets, and missing security headers.
These HTTP headers are a good starting point:
Content-Security-Policy: default-src 'self'
Strict-Transport-Security: max-age=31536000; includeSubDomains
X-Content-Type-Options: nosniff
X-Frame-Options: DENY
Referrer-Policy: strict-origin-when-cross-origin
Tailor the Content-Security-Policy to your site: if you use third-party scripts, you’ll need to allow those domains explicitly.
A03: Software Supply Chain Failures
This category is new and expands the old “vulnerable and outdated components.” It’s no longer just about libraries with known flaws, but about everything that goes into your software: dependencies, build tools, CI/CD pipelines, and even your editor extensions.
The 2024 xz Utils case illustrates it well: someone spent years earning the project’s trust and eventually slipped a backdoor (CVE-2024-3094) into a library shipped by many Linux distributions. It was discovered almost by chance, before it reached most stable releases.
Concrete measures:
- Run
npm audit(or your language’s equivalent) and enable Dependabot or Renovate. - Use lock files (
package-lock.json) and review what changes when you update. - Install only dependencies you really need, and check that they’re maintained.
- Generate an SBOM (software bill of materials) for professional projects.
A04: Cryptographic Failures
It drops to fourth place but is still serious: unencrypted sensitive data, outdated algorithms, or poorly managed keys.
- Use HTTPS across the entire site, not just on the login page.
- Store passwords with functions designed for it, such as Argon2id or bcrypt. Never use MD5 or SHA-1, and never store passwords with reversible encryption.
- Keep keys and secrets out of your source code; use environment variables or a secrets manager.
A05: Injection (SQL, XSS, and Commands)
Injection happens when user data is interpreted as code. Since 2021 it also includes XSS (Cross-Site Scripting).
// ❌ Vulnerable: the user's text is pasted into the SQL query
const sql = `SELECT * FROM users WHERE email = '${email}'`;

// ✅ Secure: parameterized query; the database treats the value as data
const { rows } = await pool.query('SELECT * FROM users WHERE email = $1', [email]);
For XSS, the rule is the same: escape output. Modern frameworks like React, Vue, and Astro do this by default; the danger appears when you insert raw HTML with functions like innerHTML or v-html.
A06: Insecure Design
This groups flaws born in planning, not in code. A perfect implementation of an insecure design is still insecure.
An example: a “forgot password” feature that sends a 4-digit code without limiting attempts. The code may be flawless, but an attacker tries all 10,000 combinations in minutes. The defense is threat modeling: asking “how would someone abuse this?” before you write code.
A07: Authentication Failures
This covers everything that lets someone impersonate a user: weak passwords, no second factor, sessions that never expire, or credential stuffing attacks (trying passwords leaked from other sites).
- Offer multi-factor authentication (MFA), at least for privileged accounts.
- Limit login attempts per account and per IP.
- Invalidate the session on the server at logout and after a password change.
- Reject passwords that appear in known breaches.
A08: Software or Data Integrity Failures
This happens when you trust code or data without verifying it wasn’t tampered with: unsigned updates, deserialization of untrusted data, or scripts loaded from a CDN that someone could modify.
If you load a library from a CDN, the integrity attribute (Subresource Integrity) makes the browser block it if its content changes:
<script
  src="https://cdn.example.com/library.min.js"
  integrity="sha384-HASH_PUBLISHED_BY_THE_LIBRARY"
  crossorigin="anonymous"></script>
A09: Security Logging & Alerting Failures
It was renamed to emphasize alerting: storing logs is useless if nobody finds out when something goes wrong.
- Log failed logins, permission changes, and server-side validation errors.
- Set up alerts for anomalous patterns, such as hundreds of failed logins in a minute.
- Never store passwords, tokens, or card data in logs.
A10: Mishandling of Exceptional Conditions
The other new category. It covers what happens when something goes wrong: unhandled errors, messages that reveal internal details, and above all systems that “fail open.”
// ❌ Fails open: if the permissions service goes down, everyone is an admin
async function isAdmin(user) {
  try {
    return await permissionsService.check(user, 'admin');
  } catch {
    return true;
  }
}

// ✅ Fails closed: when in doubt, deny access and log the error
async function isAdmin(user) {
  try {
    return await permissionsService.check(user, 'admin');
  } catch (error) {
    logger.error('Permission check failed', { user: user.id, error });
    return false;
  }
}
Show users generic error messages and keep technical details, such as stack traces, in your logs only.
OWASP Security Checklist for Your Next Project
Before you ship an application, go through this list:
- Does every endpoint check on the server that the user has permission for that resource?
- Are debug mode and default accounts disabled in production?
- Did you review dependencies with
npm auditor an equivalent tool? - Are passwords stored with Argon2id or bcrypt, and does the whole site use HTTPS?
- Are all database queries parameterized?
- Is there a limit on login and password-recovery attempts?
- Do errors fail “closed” without exposing internal details?
One detail that ties into version control: many leaks start with an API key committed to a repository by mistake. If you’re getting started with Git, see in our Git tutorial for beginners how to use .gitignore to prevent it.
Limitations of the OWASP Top 10 You Should Keep in Mind
Using the Top 10 as your only security reference is a common mistake. Keep its limits in mind:
- It isn’t exhaustive. Ten categories can’t cover every possible weakness. For full audits, use the ASVS.
- It reflects past data. The figures come from testing already done; emerging risks take time to show up, which is why two categories come from a survey.
- It’s designed for web applications. For APIs, mobile, or language models, OWASP publishes dedicated lists, such as the API Security Top 10 and the Top 10 for LLM applications.
- Automated tools aren’t enough. A scanner spots missing headers or vulnerable libraries, but not a business-logic flaw like the 4-digit code.
Web Security Starts with Design, Not with the Patch
The OWASP Top 10 2025 sends a clear message: the fastest-growing risks, such as misconfiguration and the supply chain, have less to do with brilliant code and more with discipline: reviewing permissions, dependencies, and what happens when something fails.
Check the official OWASP Top 10 2025 list to dig into each category, and the OWASP Cheat Sheets when you need the concrete fix for your language. If you want to practice web development on solid foundations, the free freeCodeCamp courses include projects that are ideal for applying this checklist.
Pick your most recent project and run it through the checklist today. Which of the 10 categories do you think student projects neglect the most? Share your take in the comments.
CuriosoTech Team
Equipo editorial de CuriosoTech. Preparamos guías de tecnología y educación con fuentes oficiales y las actualizamos cuando algo cambia.
Tags
Comments